Cybersecurity Bulletin (26 Oct – 01 Nov 2026)
Apple Vulnerabilities, Crypto Heist & Data Breaches
Reading Time: 3 Minutes
11/3/2026
The global cybersecurity landscape continues to evolve as organizations face critical software vulnerabilities, large-scale cryptocurrency theft, data breaches, ransomware attacks and targeted malware campaigns. Recent developments involving Apple WebContent, Application Integration SubWorkflow Tasks, Binance, Sony Network Communications, Moldova, SESAME, PQE Group and Asian government systems reinforce the importance of proactive vulnerability management, data protection, threat monitoring and cyber resilience.
Critical Vulnerabilities Demand Immediate Attention
Organizations should assess exposure to CVE-2026-112690, an Apple WebContent sandbox escape vulnerability that could potentially allow attackers to bypass security restrictions in affected environments.
CVE-2026-93327 involves unsafe Java deserialization in Application Integration SubWorkflow Tasks, potentially allowing remote code execution. Organizations using affected applications should prioritize risk assessment and apply vendor-recommended security updates and mitigations.
CVE-2026-117861, a sandbox escape vulnerability involving the DOM Navigation component, further highlights the importance of timely patching, browser and application security, and continuous vulnerability monitoring.
Attack Campaigns Highlight Financial and Data Security Risks
North Korea-linked hackers reportedly stole more than $6.3 billion from Binance in a record-breaking cryptocurrency heist, highlighting the growing financial impact of sophisticated cyber operations targeting digital assets.
Separately, Sony Network Communications reportedly experienced a breach exposing approximately 2.58 million customer records, reinforcing the importance of data protection, access controls and incident response preparedness.
Moldova also faced a cyberattack targeting government digital services and citizen records, demonstrating the continuing risks to public-sector infrastructure and sensitive government data.
Security Developments Reinforce the Need for Cyber Resilience
A ransomware attack on SESAME reportedly disrupted operations at the international scientific research facility, while PQE Group reported unauthorized data exfiltration involving encrypted information.
Kaspersky also reported discovering a targeted malware attack against a Windows platform used by an Asian government, highlighting the persistent threat posed by targeted cyber espionage and advanced malware campaigns.
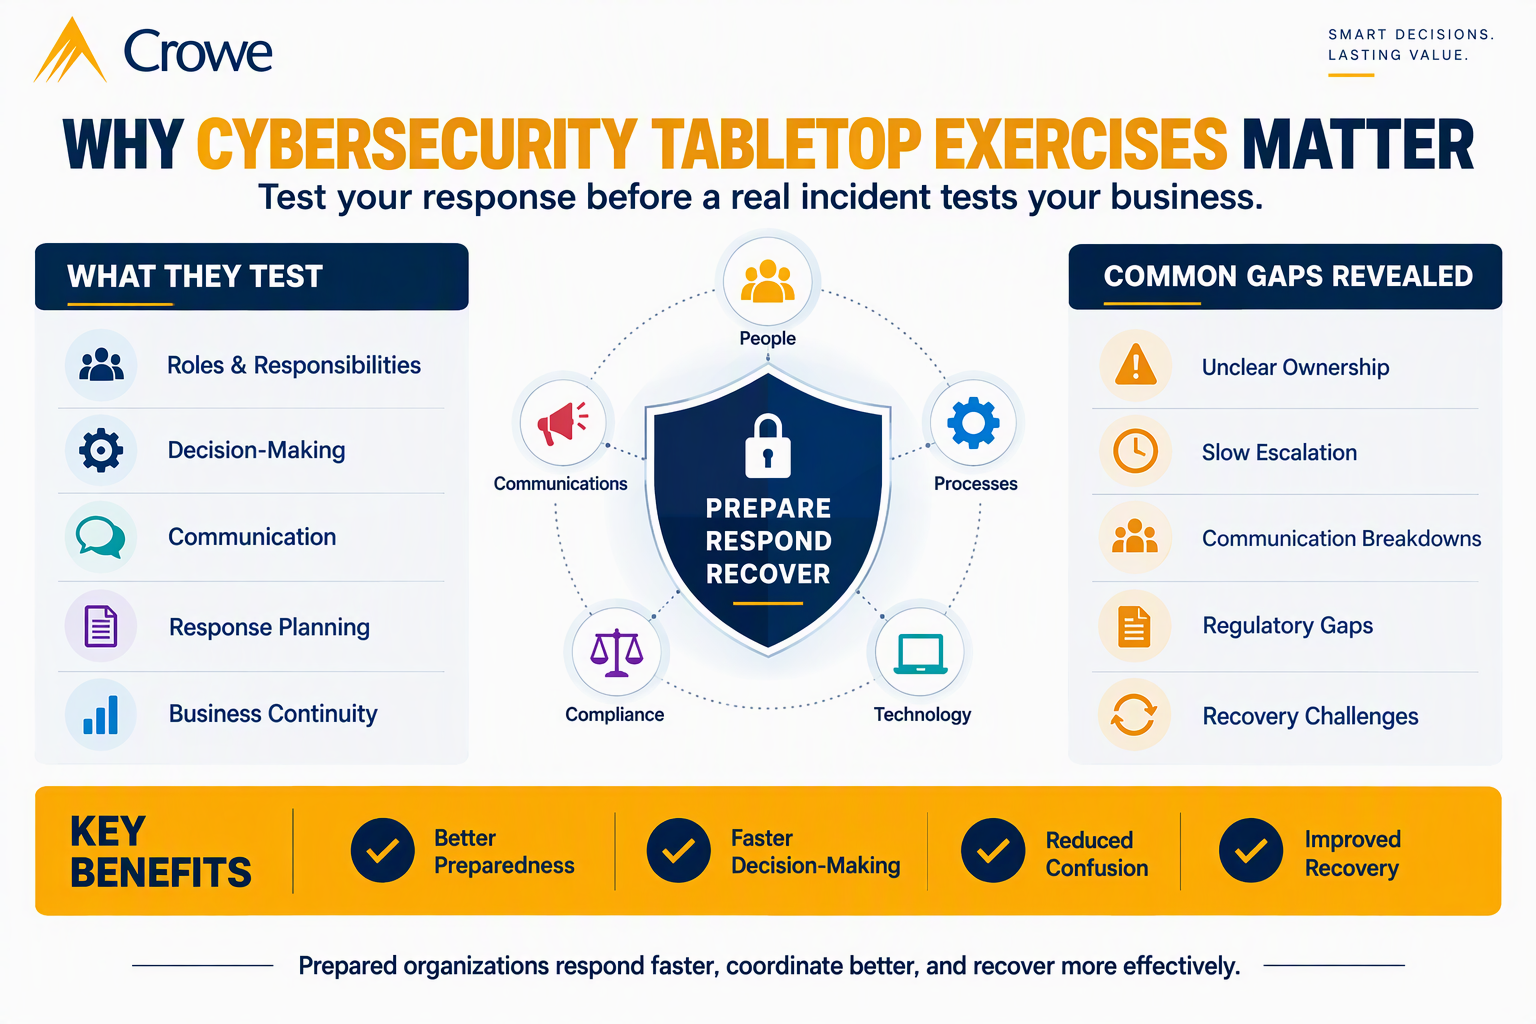
For organizations across the UAE, Middle East and global markets, these developments reinforce the need to strengthen vulnerability management, ransomware preparedness, data protection, third-party risk management, threat intelligence and incident response capabilities to reduce exposure to evolving cyber threats.
For Cybersecurity and Cyber Threat Management consulting,
Call / WA +971 52 373 4662 | [email protected]

Dawn Thomas
Senior Partner - Governance Risk & Compliance
Shahnawaz Sheik
Director – Cyber Threat Management