Cybersecurity Bulletin (17 Nov 2026)
Critical Vulnerabilities, Data Breaches and Emerging Cyber Threats
Reading Time: 3 Minutes
11/18/2026
The global cybersecurity landscape continues to evolve as organizations contend with newly disclosed vulnerabilities, credential-based attacks, data breaches, and operational disruptions. Recent developments involving NetScaler ADC, Apache HTTP Server, SAP Gateway, Red Hat Quay, Dentsu Digital, TSMC, SEGA, and Microsoft 365 underscore the importance of proactive vulnerability management, third-party risk oversight, and operational resilience.
Critical Vulnerabilities Require Immediate Attention
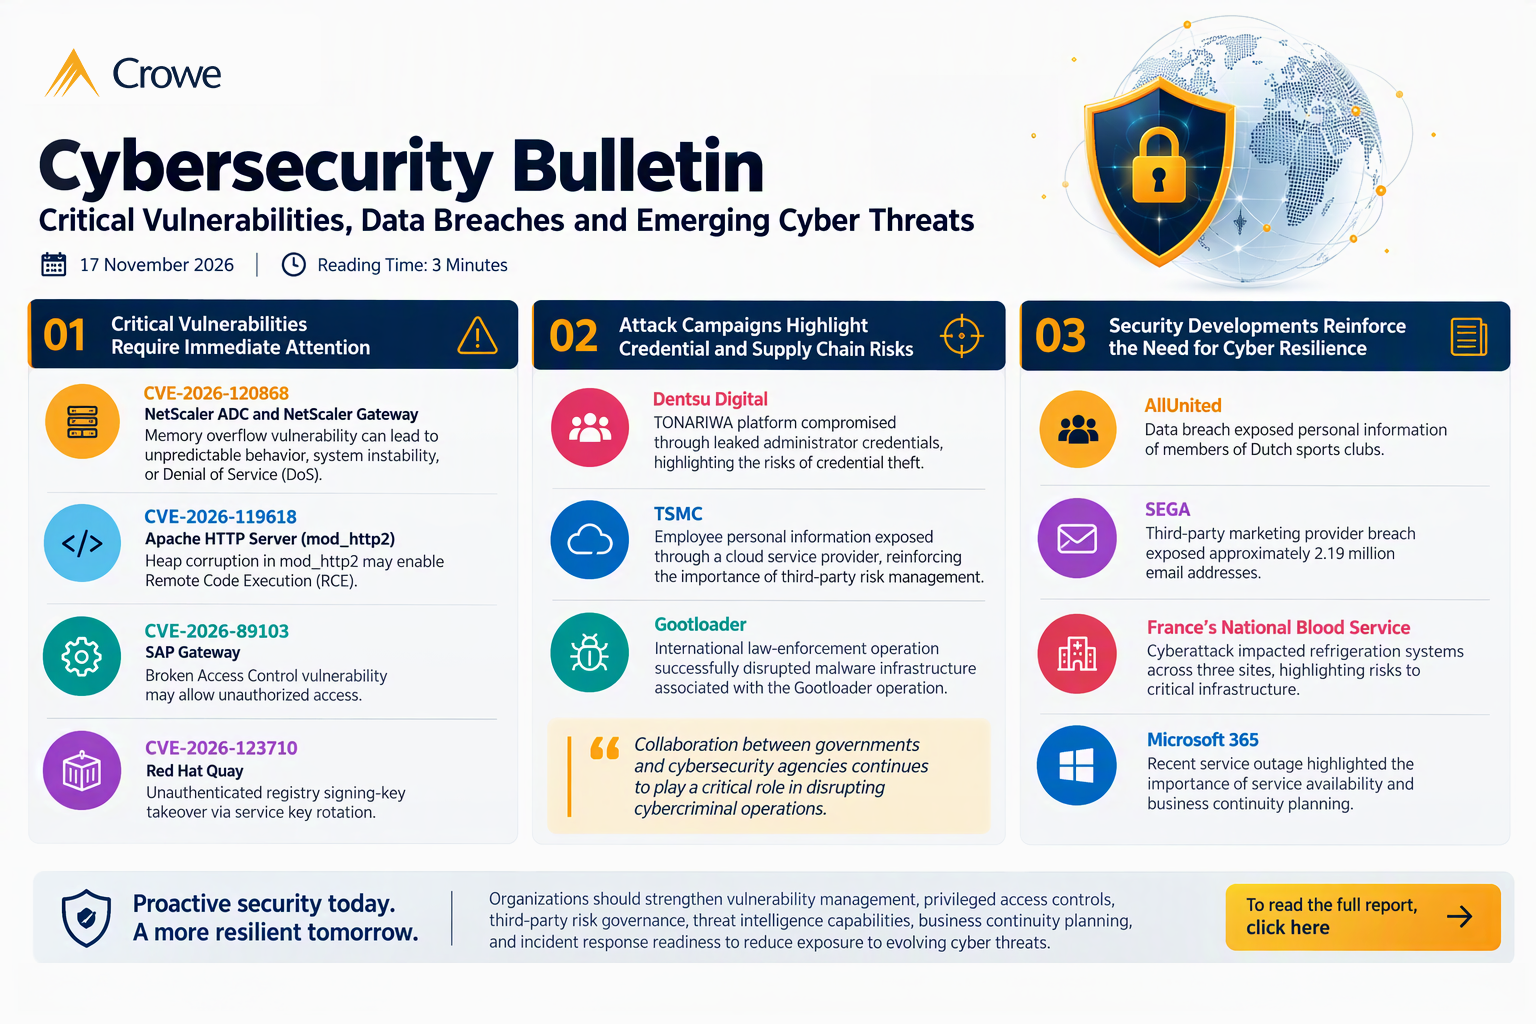
Organizations should assess exposure to CVE-2026-120868, a memory overflow vulnerability affecting NetScaler ADC and NetScaler Gateway. Successful exploitation could lead to unpredictable behavior, system instability, or Denial of Service (DoS).
Security teams should also prioritize remediation of CVE-2026-119618, a critical heap corruption vulnerability in Apache HTTP Server's mod_http2 component. The flaw may enable Remote Code Execution (RCE), potentially allowing attackers to execute malicious code on vulnerable systems.
Additionally, CVE-2026-89103 impacts SAP Gateway through Broken Access Control, while CVE-2026-123710 affects Red Hat Quay, enabling an unauthenticated registry signing-key takeover through service key rotation mechanisms. Organizations using these platforms are advised to review vendor guidance and implement recommended updates without delay.
Attack Campaigns Highlight Credential and Supply Chain Risks
Dentsu Digital's TONARIWA platform was reportedly compromised through leaked administrator credentials, emphasizing the ongoing risk posed by credential theft and inadequate access management controls.
Meanwhile, TSMC disclosed an incident involving the exposure of employee personal information through a cloud service provider, reinforcing the importance of third-party risk management and vendor security assessments.
In a significant international law-enforcement effort, authorities successfully disrupted infrastructure associated with the Gootloader malware operation, demonstrating the growing collaboration between governments and cybersecurity agencies in combating cybercrime.
Security Developments Reinforce the Need for Cyber Resilience
Several major data exposure incidents were also reported during the week. AllUnited disclosed a breach affecting members of Dutch sports clubs, while SEGA confirmed that a third-party marketing provider breach exposed approximately 2.19 million email addresses.
Critical infrastructure continues to remain a target, with France's National Blood Service reporting a cyberattack that impacted refrigeration systems across three sites. Separately, a recent Microsoft 365 service outage highlighted the security importance of service availability and business continuity planning, even when incidents are not directly linked to malicious activity.
For organizations across the UAE, Middle East and global markets, these developments reinforce the need to strengthen vulnerability management, privileged access controls, third-party risk governance, threat intelligence capabilities, business continuity planning, and incident response readiness to reduce exposure to evolving cyber threats.
For Cybersecurity and Cyber Threat Management consulting,Call / WhatsApp +971 52 373 4662 | [email protected]

Dawn Thomas
Senior Partner - Governance Risk & Compliance
Shahnawaz Sheik
Director – Cyber Threat Management