Cybersecurity Bulletin 02-08 November
Critical Apache Juneau Flaws, Education Sector Data Breaches and Emerging Cyber Threat
Reading Time: 3 Minutes
11/11/2026
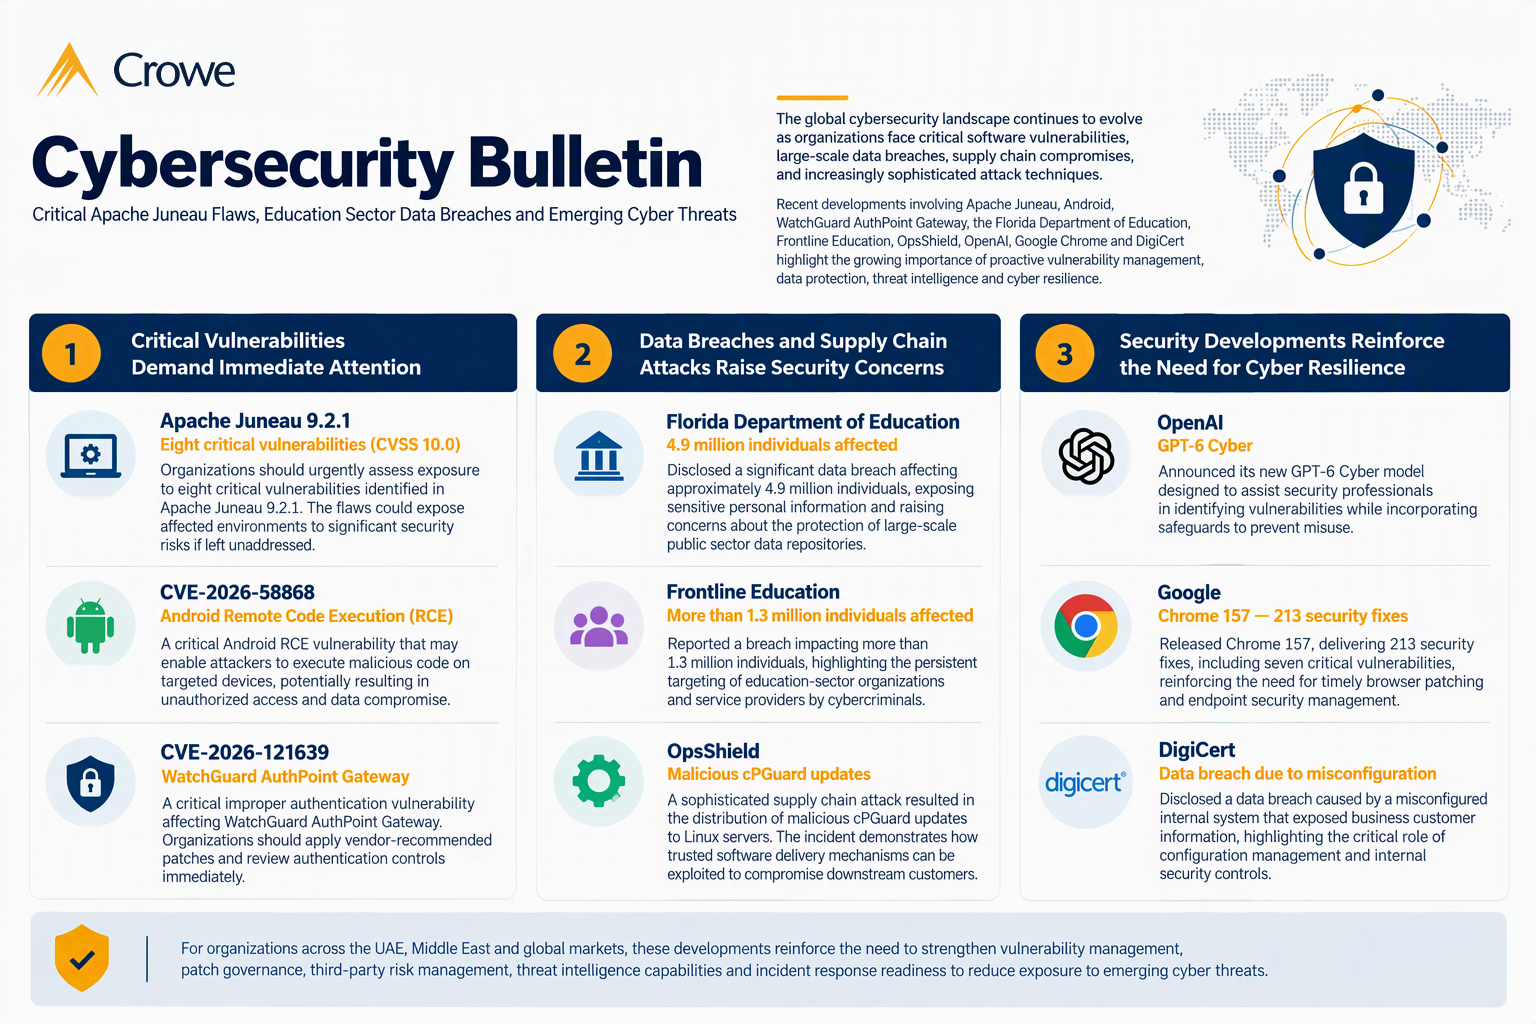
The global cybersecurity landscape continues to evolve as organizations face critical software vulnerabilities, large-scale data breaches, supply chain compromises, and increasingly sophisticated attack techniques. Recent developments involving Apache Juneau, Android, WatchGuard AuthPoint Gateway, the Florida Department of Education, Frontline Education, OpsShield, OpenAI, Google Chrome and DigiCert highlight the growing importance of proactive vulnerability management, data protection, threat intelligence and cyber resilience.
Critical Vulnerabilities Demand Immediate Attention
Organizations should urgently assess exposure to eight critical vulnerabilities (CVSS 10.0) identified in Apache Juneau 9.2.1. The flaws represent one of the most severe vulnerability disclosures of the year and could expose affected environments to significant security risks if left unaddressed.
Security teams should also prioritize remediation of CVE-2026-58868, a critical Android Remote Code Execution (RCE) vulnerability that may enable attackers to execute malicious code on targeted devices, potentially resulting in unauthorized access and data compromise.
Additionally, CVE-2026-121639, a critical improper authentication vulnerability affecting WatchGuard AuthPoint Gateway, underscores the growing importance of securing identity and access management infrastructure. Organizations using affected systems should apply vendor-recommended patches and review authentication controls immediately.
Data Breaches and Supply Chain Attacks Raise Security Concerns
The Florida Department of Education disclosed a significant data breach affecting approximately 4.9 million individuals, exposing sensitive personal information and raising concerns about the protection of large-scale public sector data repositories.
In a separate incident, Frontline Education reported a breach impacting more than 1.3 million individuals, highlighting the persistent targeting of education-sector organizations and service providers by cybercriminals seeking valuable personal information.
Meanwhile, a sophisticated supply chain attack involving OpsShield resulted in the distribution of malicious cPGuard updates to Linux servers. The incident demonstrates how trusted software delivery mechanisms can be exploited to compromise downstream customers and emphasizes the importance of software supply chain security monitoring.
Security Developments Reinforce the Need for Cyber Resilience
In industry news, OpenAI announced its new GPT-6 Cyber model designed to assist security professionals in identifying vulnerabilities while incorporating safeguards to prevent misuse.
Google released Chrome 157, delivering 213 security fixes, including seven critical vulnerabilities, reinforcing the need for timely browser patching and endpoint security management.
Additionally, DigiCert disclosed a data breach caused by a misconfigured internal system that exposed business customer information, highlighting the critical role of configuration management and internal security controls.
For organizations across the UAE, Middle East and global markets, these developments reinforce the need to strengthen vulnerability management, patch governance, third-party risk management, threat intelligence capabilities and incident response readiness to reduce exposure to emerging cyber threats.
For Cybersecurity and Cyber Threat Management consulting, Call / WA +971 52 373 4662 | [email protected]

Dawn Thomas
Senior Partner - Governance Risk & Compliance
Shahnawaz Sheik
Director – Cyber Threat Management