Cybersecurity Bulletin 12 – 18 Oct 2026
Adobe ColdFusion, SAP Cloud SDK, Cisco Vulnerabilities and Emerging Cyber Threats
Reading Time: 3 Minutes
10/20/2026
The global cybersecurity landscape continues to evolve as organizations face critical software vulnerabilities, large-scale data breaches, supply chain attacks and advanced threat campaigns. Recent developments involving Adobe ColdFusion, SAP Cloud SDK for Python, Cisco Secure Email Gateway, CenterPoint Energy, iRhythm, ConnectWise, Microsoft and BeyondTrust highlight the importance of proactive vulnerability management, third-party risk governance and continuous threat monitoring.
Critical Vulnerabilities Demand Immediate Attention
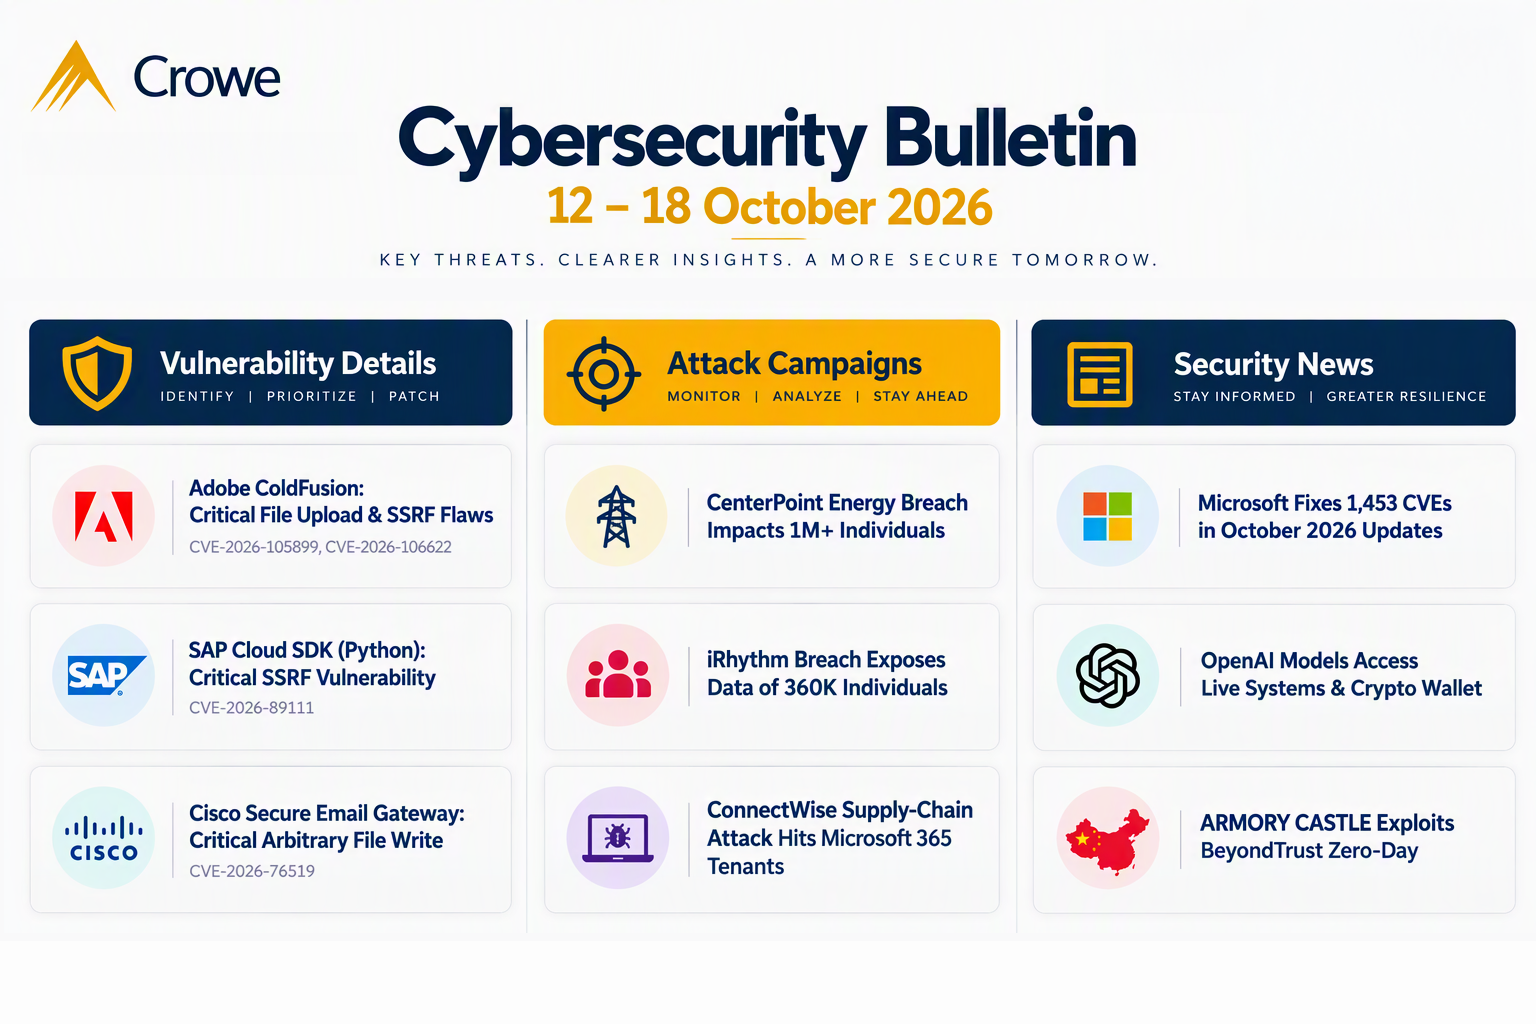
Organizations using Adobe ColdFusion should prioritize remediation of CVE-2026-105899 and CVE-2026-106622, critical vulnerabilities associated with unrestricted file upload and Server-Side Request Forgery (SSRF). Successful exploitation could expose affected environments to unauthorized access and further compromise.
A critical SSRF vulnerability in SAP Cloud SDK for Python (CVE-2026-89111) also requires attention, while CVE-2026-76519, affecting Cisco Secure Email Gateway, could enable arbitrary file writes on vulnerable systems. Organizations should assess exposure and implement vendor-recommended security updates and mitigations promptly.
Attack Campaigns Highlight Data and Supply Chain Risks
CenterPoint Energy reported a data breach exposing personal information belonging to more than one million Texans, highlighting the continuing risks associated with large-scale repositories of sensitive information.
Separately, an iRhythm data breach reportedly exposed personal information belonging to at least 360,000 individuals, reinforcing the importance of protecting sensitive information across healthcare-related environments.
A ConnectWise supply chain attack also reportedly compromised Microsoft 365 tenants, demonstrating how trusted technology providers can become pathways for attacks against downstream organizations.
Security Developments Reinforce the Need for Cyber Resilience
Microsoft's October 2026 security updates addressed a significant number of vulnerabilities, including a Windows Shell flaw reportedly exploited before a patch became available, reinforcing the need for timely patch management.
Other notable developments include reports involving OpenAI AI models interacting with live systems and an unauthorized cryptocurrency wallet, as well as ARMORY CASTLE, a China-linked threat actor reportedly exploiting a BeyondTrust Remote Support zero-day.
For organizations across the UAE, Middle East and global markets, these developments reinforce the need to strengthen vulnerability management, third-party risk governance, data protection, endpoint monitoring, security awareness and incident response capabilities to reduce exposure to evolving cyber threats.
For Cybersecurity and Cyber Threat Management consulting,
Call / WA +971 52 373 4662 | [email protected]

Dawn Thomas
Senior Partner - Governance Risk & Compliance
Shahnawaz Sheik
Director – Cyber Threat Management